In 2027, the Swiss e-ID will become a reality. It is the key to a trustworthy digital identity that will lay the foundations for optimizing many processes that are complicated, inefficient, or not fully digital today.
What does the e-ID mean for Swiss companies? How is it related to the swiyu trust infrastructure? And what else do organizations need to know?
We will answer these and other key questions in the first part of this blog post. In the FAQ in the second part, we’ll delve deeper into specific topics such as the e-ID timeline and strategy, rights and duties, technology and integration – so that companies have the necessary basic understanding and can look forward to 2027 with confidence.
Everything clear?
Find out easily by testing your knowledge in our interactive quiz (German only)!
What is the Swiss e-ID?
The e-ID is a state-issued digital ID Swiss residents can use in both the digital and the real world. Any person who has a Swiss identity card, a Swiss passport, or an alien’s identity card issued by the Swiss government can apply for an e-ID. Its use is voluntary and free of charge.
How does the Swiss e-ID work?
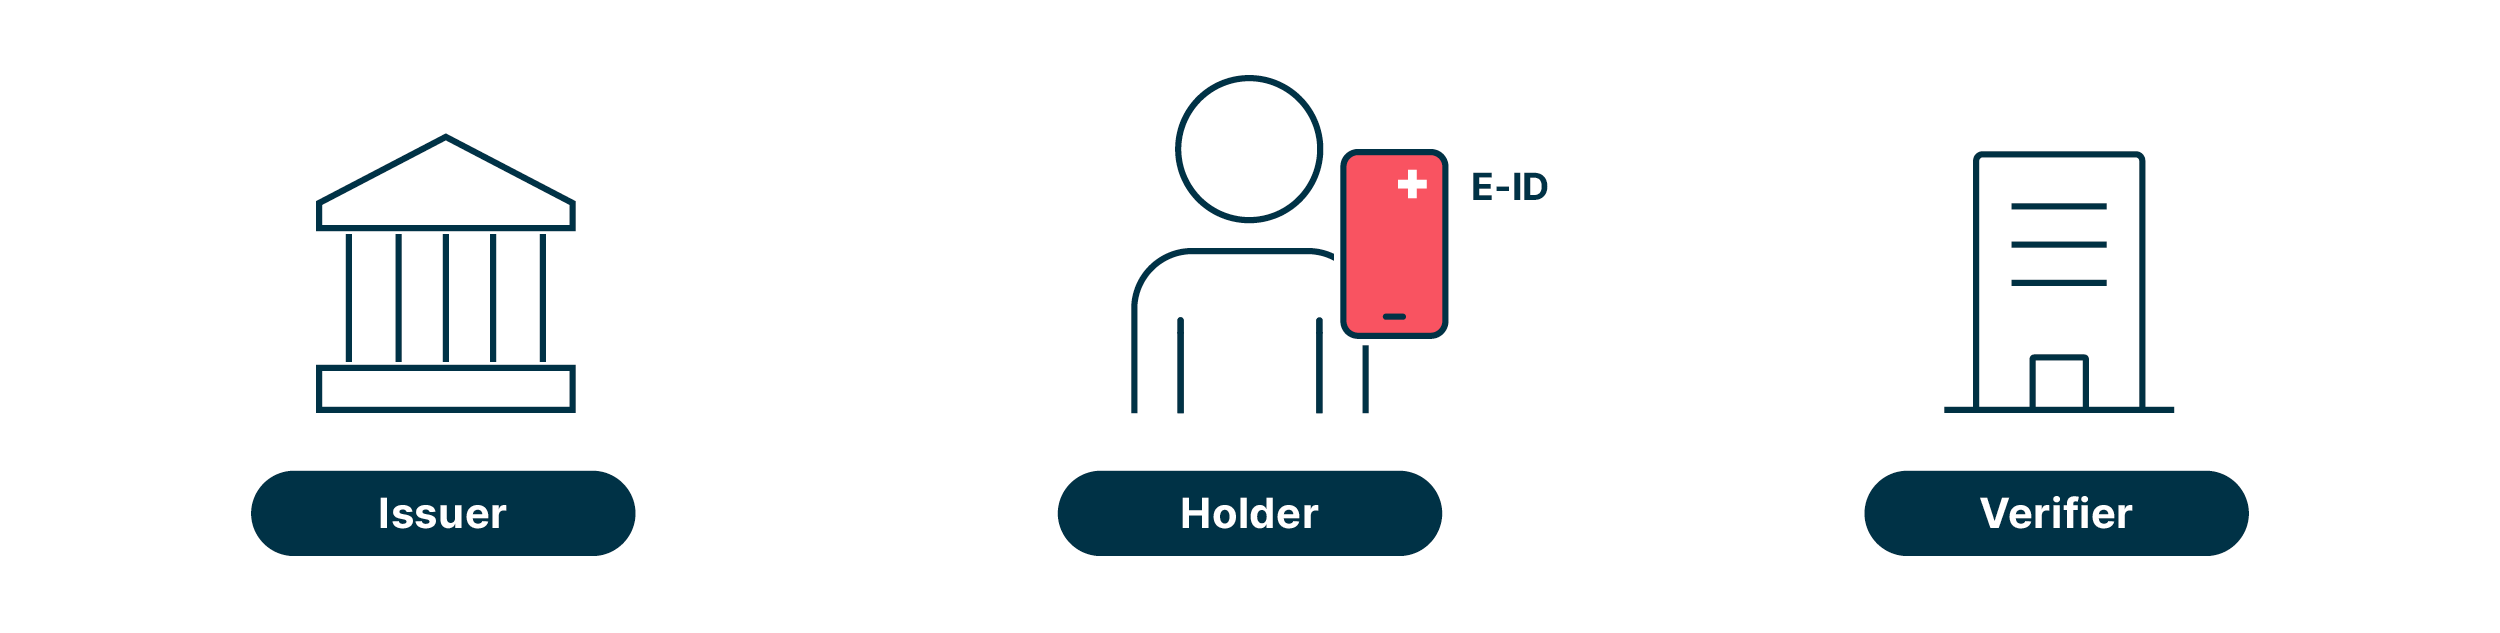 Just like with a paper ID, there are always three parties involved:
- Issuer
The issuer (federal government) verifies the identity and issues a digitally signed credential, making it forgery-proof. - Holder
The holder stores the credential in their smartphone app, the so-called wallet. It is stored exclusively there, not in a centralized federal database. - Verifier
The verifier (e.g., a company or an authority) requires the information needed. The holder sees who asks for what and actively discloses the attributes. The verifier uses the signature to ensure that the attributes are valid and have not been modified, without having to check with the federal government.
The e-ID can be used in any situation where identity verification is required today.This is particularly helpful in the digital environment, where users currently have to upload a copy of their ID, complete a video identity verification, or have a document reviewed manually, e.g.,
- Onboarding and account opening
Identification within seconds using immediately machine-readable, verified data instead of video call or postident - Proof of age
For sales and access to age-restricted offerings without the provider seeing the customer’s date of birth and name - Access control for sensitive processes
Change of address, termination of contract, payments, resetting access rights - Initial identification for customer account
One-time identification via e-ID, then log in as usual
What requirements must a company meet with regard to e-ID?
In order for a company to verify an e-ID, it must take several factors into account:
Organization
It needs to be defined in which process the e-ID will be used and which attributes are actually required for that purpose. The verifying party may only request the attributes necessary for that specific case. For proof of age, for example, this means age, and not the name and address as well. In addition, it must be clarified whether an alternative option should be available for people without an e-ID and what it would consist of. The use of the e-ID is optional. Without offering an alternative, the customer base for one’s services will shrink.
Technology
A separate component is needed to send the request to the wallet and verify the response. The federal government provides open-source components for this purpose, but not a ready-made platform where you can simply sign up and get started. Plus, the organization must enroll in the government registry so that the other party can identify who is actually making the request. This is an integration project that requires time to set up, not a simple configuration task.
Legal
The company’s own regulations, terms and conditions, and procedural guidelines must be reviewed to determine whether they allow for digital identification. Phrases such as «file a copy of the ID» otherwise prevent its use from the outset. Anyone who accepts the e-ID must also continue to accept a physical ID when an individual appears in person. For authorities and entities performing public functions, there is an additional legal obligation to accept the e-ID, subject to a deadline.
Expertise
The e-ID does not contain a unique identifier. It can be used for identification, but not for logging in. Anyone who wants to recognize returning users must identify them once using the e-ID and then create a separate account for them. Only the public sector is allowed to use the OASI number as a unique identifier.
Time
The e-ID will be launched in 2027; a test environment is currently available. Those who want to take advantage of the e-ID as soon as possible should now plan its integration and test the processes.
The swiyu trust infrastructure
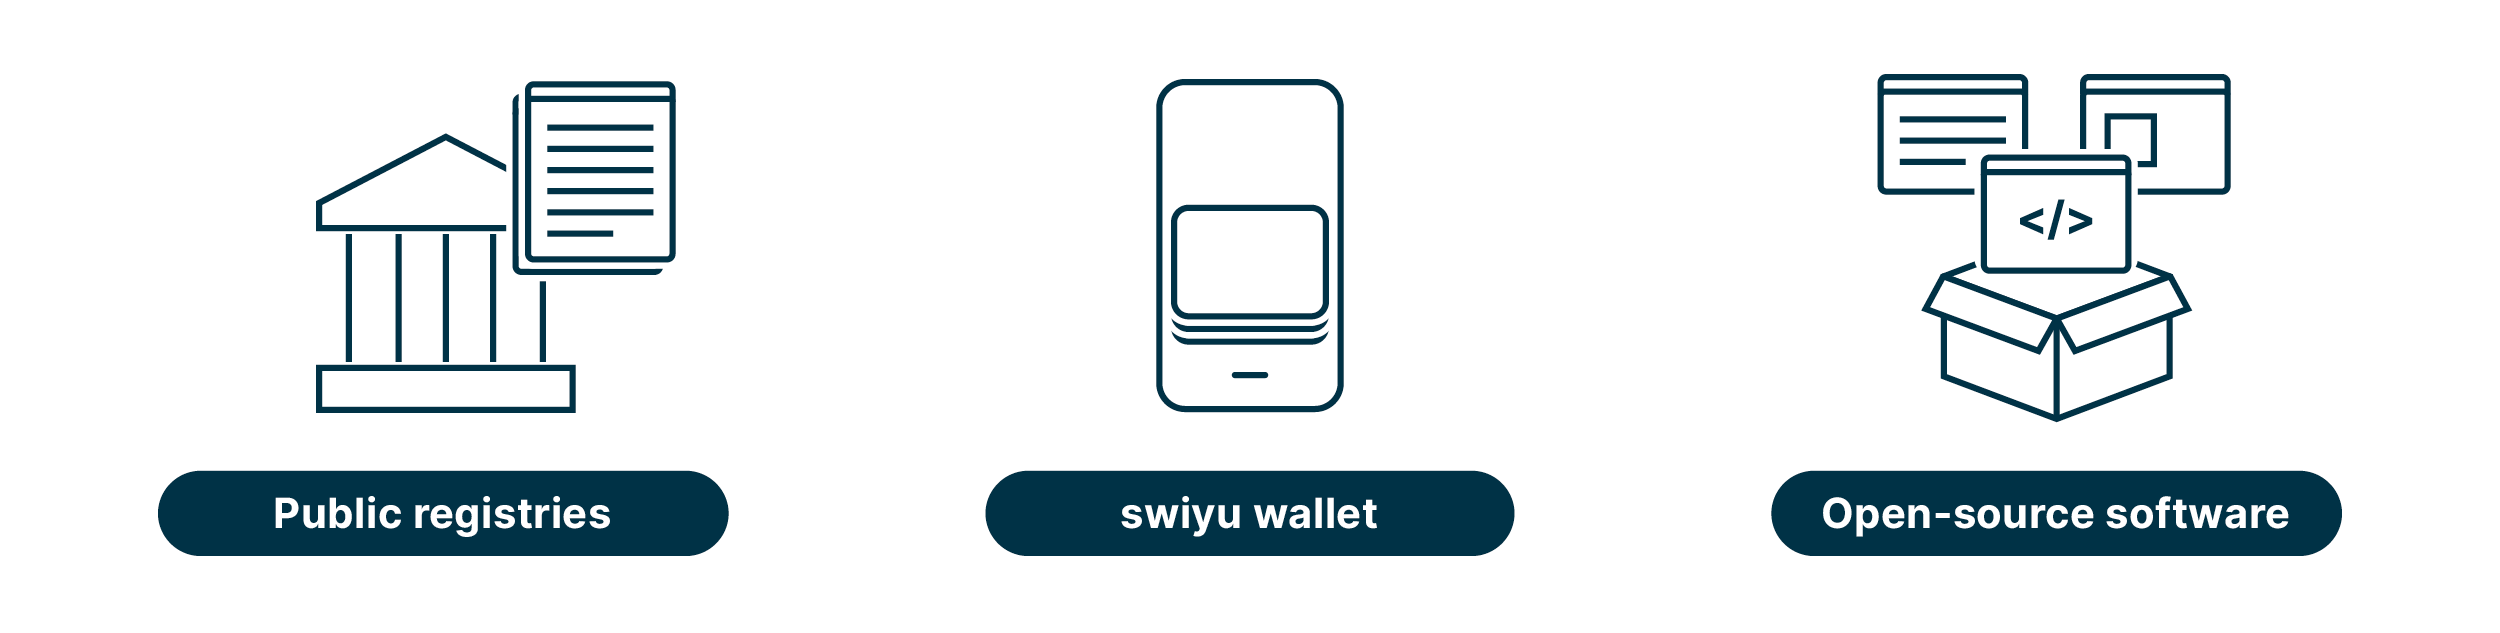
swiyu is a made-up word for the federal trust infrastructure. The federal government provides the following components:
-
Public registries for the verification of credentials,
-
the swiyu wallet for Android and iOS, and
-
open-source software for issuing and verifying credentials.
What role does the trust infrastructure play in the Swiss e-ID system?
The swiyu trust infrastructure will serve as the foundation for issuing and using the Swiss e-ID. In particular, it will only be possible to issue the e-ID in the swiyu wallet (at least initially). What other benefits provides the swiyu trust infrastructure?
The e-ID is only one among many credentials using swiyu. Based on the same infrastructure, cantons, communities, and private organizations can issue their own digital credentials, ranging from drivers’ licenses to diplomas and member cards.
The next step: from basic understanding to individual use case
The Swiss e-ID and the swiyu trust infrastructure serve as the foundation for an ecosystem in which digital credentials can be reliably issued, stored, and verified. For businesses, therefore, it is not only the e-ID itself that is relevant, but also the question of what role they can play in the future: as verifiers, issuers of their own credentials, or users of more efficient digital processes.
The next step is the systematic analysis of one’s own organization: Where do we still identify people manually today? Which credentials do we already issue or review on a regular basis? Where do paper documents, PDFs, or e-mails cause media disruption, delays, or risks?
These questions can be used to identify initial use cases that allow for a functional, legal, and technical assessment. Combined with the more detailed information in Part 2 of this blog, this basic understanding of e-ID and the trust infrastructure will serve as a concrete roadmap for preparing for 2027.
Check out our FAQ to learn more, and test your knowledge with our interactive quiz (German only).
Book a free 30-minute consultation on the e-ID and swiyu trust infrastructure
Talk to a specialistFAQ
What is swiyu, what is the e-ID?
Is swiyu the same as the e-ID?
swiyu is the name of the Swiss trust infrastructure (wallet app, base registry, trust registry, standards, and reference implementations). The e-ID is just one credential that can be used on this infrastructure. There will be many others, e.g., driver’s license, confirmation of place of residence, diplomas, or membership cards. This is also the reason why the infrastructure can go live before the e-ID is available.
Is a very large amount of money being spent here just on the e-ID?
The investment (approx. 182 mio. Swiss francs for setup and pilot projects, followed by approx. 25 mio. Swiss francs in annual operating costs) will go to a generic trust infrastructure that the federal government, cantons, municipalities, and private entities can use for any type of credentials. The e-ID is the most well-known use case, but not the only one. The term «ecosystems» is used deliberately.
Will only Swiss citizens be eligible for an e-ID?
Any person who has a Swiss identity card, a Swiss passport, or an alien’s identity card issued by the Swiss government can apply for an e-ID. For companies this means that also employees and customers who do not have Swiss citizenship but do have a residence permit are part of the target group. The e-ID contains information about the type of identification document on which it is based.
Is the federal government the only entity authorized to issue electronic credentials?
The federal government issues the e-ID and operates the infrastructure. Cantons, municipalities, and private organizations may issue and verify their own credentials on that infrastructure: diplomas, extracts from the debt collection register and other registries, staff badges and membership cards, tickets, permits, and warranties. That is the reason for the expected high economic benefits.
Do you still need an e-ID if you have AGOV?
AGOV is the authentication service of the Swiss authorities and thus a login. The e-ID is a proof of identity, no login (see below). However, it will be possible to use the e-ID and presumably additional credentials with AGOV. Specifically, this means that applications connected to AGOV will be able to retrieve information from the e-ID or other forms of digital credentials that will be supported in the future. As a result, many public service applications will be able to use the e-ID very easily, provided they use AGOV.
Timeline and strategy
Will the e-ID be introduced in phases?
The trust infrastructure is expected to go live in the first half of 2027. Other credentials can be issued starting then. The e-ID will follow later. The exact date is still unknown.
There is some confusion here because there is also mention of three «levels of ambition»: 1. the e-ID, 2. other credentials issued by the public sector, and 3. credentials issued by the private sector. However, according to the current status, both the public sector and the private sector will be able to issue and use additional credentials once the trust infrastructure goes live. Therefore, ambition levels 2 and 3 can be developed first, while ambition level 1 will follow later.
Nevertheless, the concept of ambition levels is useful: Although credentials can be issued and used immediately, standardization and ecosystem-specific characteristics are important and will present a challenge for ambition level 2 and, in particular, level 3.
Will the launch of the e-ID be postponed so that we can wait and see?
The infrastructure is expected to go live in the first half of 2027. Anyone who waits until then to address the issue will miss the lead time: schema design, process adjustments, legal review, integration, and testing in the public beta all take months. For public authorities, there is also a legal obligation to accept the e-ID. The postponement provides a window of opportunity for preparation – it’s no reason for inaction.
Do we have to wait on everything until the e-ID is available?
There are three time frames: Public beta is now available for integration and testing (with no legal effect). Starting in H1 2027 (expected), credentials will be accepted for use in productive environments if the issuing organization can verify the individual’s identity through other channels, such as diplomas, staff badges, permits, or other forms of verification. Use cases that intend to use the e-ID itself as a reference identity will follow at a later date.
Rights and duties
Do we need to support the e-ID at all?
For private companies, there is no legal obligation to accept the e-ID. However, for authorities and other entities that perform public functions, there is. They must accept the e-ID when verifying a person’s identity in line with federal law, no later than two years after the relevant provision takes effect (art. 23 and 34 e-ID Act). This also applies to cantons, municipalities, and private entities that perform public functions (e.g., in the healthcare sector). Anyone who accepts the e-ID must also continue to accept a physical ID when an individual appears in person. For private entities, the following applies: «you don’t have to» doesn’t mean «you shouldn’t». Where competitors offer seamless identification across platforms, manually uploading copies of identification documents quickly becomes a disadvantage. Plus, data protection is easier to ensure and prove when using the e-ID, since the necessary attributes can be specifically requested.
Can we use the e-ID on a platform provided by the federal government?
The federal government will provide the infrastructure (registry, wallet) and open-source reference implementations for issuers and verifiers, but no ready-to-use platform including account and click integration. Anyone who wants to issue or verify credentials will operate their own issuer/verifier components, register their own identity in the base registry, go through a verification process, define schemas, and adapt their own business processes. This is an integration project involving technical, organizational, and legal work packages – it’s not a trivial task that can be completed in a week.
Data protection and security
Will the federal government store all credentials in a centralized database?
Credentials are exclusively stored in the wallet on the holder’s device (decentralized data storage). There is neither a centralized credential database nor a user registry. Holders do not even have their own identifier (DID) in the system. Only issuers and verifiers are entered in the registry.
Will the government see when and where I present my credentials?
The verification process takes place directly between the wallet and the verifier without consulting the issuer or the federal government. Plus, the validation process is designed to prevent any traces of use: The revocation information (token status list) is retrieved as a complete list, so that the issuer cannot determine whose credential is being verified or where.
As an issuing organization, will we be able to see where our credentials are used?
The «privacy by design» principle works both ways: The issuer doesn’t get any information about how the credentials are used either. Any issuer that wants to build business models on usage analytics («we see where our credential is used») is ignoring the architecture. Insights into usage arise only when the issuer itself acts as the verifier.
Is it easier to be tracked online when you use an e-ID?
Compared to current identification methods (copy of ID, e-mail address, phone number for each provider), the system complies with the data minimization principle: Only the requested attributes are disclosed, and neither the government nor the issuer can see how they are used. In addition, the e-ID does not have a unique identifier. A verifier thus cannot determine whether an e-ID has been used with them before. One exception is the use of e-ID in the context of public services: In this case, the (unique) OASI number can be queried, which allows for user recognition.
Is the usage of the e-ID completely anonymous and unlinkable?
Is the usage of the e-ID completely anonymous and unlinkable?
The design minimizes the information that the government and issuers can monitor, but claiming it is «completely anonymous» is a stretch. Disclosed attributes are visible to the verifier in plain text. However, the new infrastructure will make it easier for users to control who they share their data with and to report misuse.
Method and integration
Can the e-ID be used as login?
Technically, a login-like process can be set up using a credential request. However, the e-ID is a proof of identity, not an authentication or SSO service: There is no session management, no federation, no «login with e-ID» protocol, and (for private organizations) no unique identifier to recognize an e-ID. For recurring logins, this combination makes sense: one-time identification via e-ID during onboarding, followed by a traditional authentication method (e.g., AGOV with public authorities, which acts as the e-ID verifier itself).
Is it possible to combine attributes from multiple credentials in a single presentation?
Currently, a verifier cannot request a single presentation that combines attributes from multiple credentials (e.g., name from the e-ID plus diploma attribute in a single step), and the swiyu wallet cannot generate such a presentation. The common workaround is to make sequential, separate presentation requests. Anyone designing processes that require multiple credentials must factor this into the UX and architecture.
Does the wallet allow users to see whether a verifier or issuer is trustworthy?
The trust registry and trust statements for issuers and verifiers exist. The processing and display of these statements in the wallet on the user's end is not yet complete. The system verifies that you are interacting with an organization listed in the commercial register and, with regard to e-ID, that this organization does not request any unnecessary data. This will be sufficient for many use cases.
Is swiyu based on blockchain?
swiyu does not use blockchain. Issuer and verifier identities are based on did:webvh, which features a cryptographically verifiable change history, hosted on the federal base registry. As a result, entries cannot be modified.
International perspective
Is the Swiss e-ID compatible with the EU and other countries?
As of today, there is no compatibility with the EUDI wallet and no mutual legal recognition. However, Switzerland relies on the same family of open standards as the EU (OID4VCI, OID4VP, SD-JWT VC), which keeps the technical gap small, and international interoperability is a clear goal.
Are there any international use cases that cannot be implemented using the Swiss infrastructure?
The verification of Swiss credentials is not limited to Switzerland: Anyone who implements the open standards and queries the public registries can verify Swiss credentials worldwide, e.g., diplomas or certificates from universities or employers. Another option is to use the Swiss infrastructure for one’s own sector-specific international trust services. This allows organizations to maintain their own trust registries to identify, e.g., financial and healthcare providers or colleges and universities. While the federal government ensures technical trust, trust in the content is established through these trust registers.
Business models and opportunities
Isn't the infrastructure just a cost factor, without enabling any new business models at all?
A government-operated open trust infrastructure drastically reduces the costs of trustworthy data exchange. This results in business models: Reusable identification and KYC (know your customer – verified once, used multiple times), data-minimizing age verification, machine-verifiable B2B credentials (powers of attorney, registry extracts, certifications) as a basis for process automation, issuance of proprietary credentials as a tool for customer retention and efficiency, as well as services related to integration, schema design, and verification for third parties. Early adopters will fill these roles before they become standard.
Does every company have something it could issue?
Almost every organization already issues credentials today – just in the form of paper, PDFs, or plastic cards: employment references and employer confirmations, staff and access badges, customer and membership cards, course certificates, warranty documents, insurance certificates, or tickets. Each of these proofs, which someone currently has to check manually, type up, or request via e-mail, is a candidate for verifiable credentials. The question is not whether an organization has anything to issue, but rather which evidence requires the most effort on the part of third parties to verify and is therefore particularly valuable.